

TISAX®: Order in 2026 or be assessed against VDA ISA2027?
The new TISAX® assessment catalogue VDA ISA2027 has been published since July 2026. It applies to all assessments ordered from 1 January 2027. If you are planning an initial or follow-up assessment in the coming months, the date of your order therefore also determines the catalogue. Our guide sets out both options with their pros and cons.
In brief
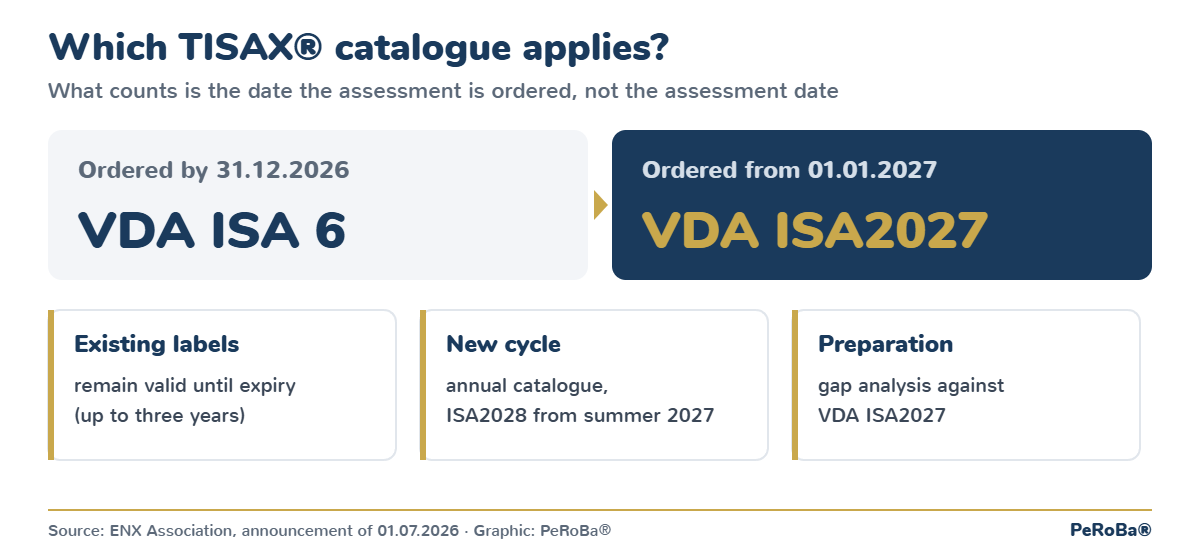
What counts is the date the assessment is ordered, not the date it takes place. Assessments ordered by 31.12.2026 follow VDA ISA 6; those ordered from 01.01.2027 follow VDA ISA2027. Existing labels remain valid until they expire. There is no generally right choice: what matters is your customer’s requirement, the expiry of your label and the maturity of your information security management.
What ENX has announced
On 1 July 2026, around ten years after the first TISAX registrations, the ENX Association announced the publication of VDA ISA2027. The catalogue applies to all TISAX assessments ordered from 1 January 2027. Labels already issued remain valid for their full term of up to three years.
A new annual cycle has also been introduced: catalogues now carry a year instead of a version number, are published each summer and apply to assessments ordered from 1 January of the following year. ISA2028 is announced for summer 2027. According to ENX, this does not mean companies have to be assessed more often.
What changes in ISA2027
- Prototype protection: The previous control groups are merged into two areas, organisational requirements and physical and environmental security. There will be two prototype protection labels, Basic and Facilities, with Facilities including all requirements of Basic. New requirements cover the traceability and lifecycle of protected vehicles, components and parts through to disposal, return or recycling as specified by the customer.
- Information security: Many requirements have been clarified, and some “should” requirements become “must” requirements. Where the catalogue lists aspects, each aspect must be consciously considered and the implementation decision explained in the assessment.
- Suppliers: For high protection needs, supplier assessment gains weight. For very high protection needs, evidence is required in the form of a TISAX label, an equivalent third-party assessment or a suitable supplier audit.
- Standard references: The mapping to ISO/IEC 27001:2022 has been reviewed and references to the 2013 edition removed. Mappings to the NIST Cybersecurity Framework 2.0 have been updated and those to IEC 62443 clarified.
- Managers are explicitly named as a target group for awareness and training.
Option 1: Order in 2026
In favour:
- You are assessed against the familiar VDA ISA 6 catalogue, to which your documentation and evidence are already aligned.
- No additional transition effort before the assessment.
- Planning certainty if your label is due soon or a customer requires it at short notice.
Against:
- The window until 31 December is short. Clarify with your audit provider which date counts as the order and have it confirmed in writing.
- The transition effort is postponed, not avoided: the next assessment will follow the catalogue current at that time.
- Ordering early does not help if your organisation is not yet ready for the assessment.
Option 2: From 2027 against VDA ISA2027
In favour:
- Your label is based on the current catalogue, and your management system is already aligned with the new requirements.
- You gain time for orderly preparation.
Against:
- A gap analysis is needed before the assessment, especially for changed “must” requirements, prototype protection and supplier evidence.
- The English version of the catalogue is authoritative; according to ENX, further translations will follow in the coming months.
Five questions for your decision
- By when does your customer require a valid label, and when does your current label expire?
- How up to date are your documentation and evidence measured against VDA ISA 6?
- Do you need a prototype protection label? Then the new structure affects you in particular.
- How robust is your evidence of supplier management for high and very high protection needs?
- Do you have internal resources for a gap analysis before the assessment?
PeRoBa® recommendation
Decide based on customer requirements and maturity, not on the catalogue alone. Whichever option you choose, a gap analysis against VDA ISA2027 is worthwhile: with the annual cycle, alignment with the current catalogue becomes an ongoing task.
PeRoBa® supports companies in preparing for TISAX assessments, from gap analysis and internal audits to evidence management, in line with our principle of helping you help yourself. Arrange a free, no-obligation initial consultation.
Editorial sources: ENX Association, announcement of 1 July 2026 on the publication of VDA ISA2027; additional published explanations by audit providers on the prototype protection label structure. Status: 9 November 2026. This article replaces neither the catalogue itself nor binding information from ENX or your audit provider. TISAX® is a registered trademark of the ENX Association. Graphics: PeRoBa®.